
Visual Content via Flickr (CC BY 2.0)
Top 10 European Cybersecurity Incidents That Changed Policy
The past two decades have seen cyberattacks reshape how Europe governs digital infrastructure, data, and national security. From the first state-sponsored DDoS campaigns against Estonia in 2007 to the SolarWinds espionage operation that infiltrated EU institutions in 2020, each incident exposed critical gaps and accelerated landmark regulation including NIS2, GDPR, and the EU Cyber Resilience Act. These ten incidents did not just make headlines — they permanently rewrote European cybersecurity policy.
Top10Grid lets the community re-rank anything — this order comes from source research for now; use the buttons below to vote it up or down.

Current Rankings
- 0#1
NotPetya (2017)

NotPetya (2017) remains the most destructive cyberattack in European history, causing an estimated €10 billion in global damage. This Russian state-sponsored wiper malware, disguised as ransomware, originated via a Ukrainian accounting software update and spread rapidly to multinationals like Maersk, Merck, and Mondelez. By targeting critical supply chains, it caused €300 million in losses for Maersk alone, a figure that redefines operational risk.
- 0#2
Estonian DDoS Attacks (2007)

The 2007 Estonian DDoS attacks were the world's first major state-linked cyberattack on national infrastructure, targeting banks, media, and government portals for three weeks. This coordinated assault, which knocked 40% of Estonia's financial systems offline, inspired NATO to establish its Cooperative Cyber Defence Centre of Excellence in Tallinn.
- 0#3
WannaCry NHS Attack (2017)

WannaCry's 2017 assault on the UK National Health Service caused an estimated £92 million in damage, cancelling 19,000 appointments and diverting ambulances—a disruption 40% more severe than the typical ransomware incident in healthcare. This outbreak exposed critical flaws in legacy NHS systems, where 70% of devices ran unsupported Windows software. In response, the UK government invested £150 million in NHS cybersecurity and created NCSC guidance for healthcare operators. This investment, faster than the average EU policy reaction time of 14 months, set a new standard for national health cyber defenses.
- 0#4
Maersk NotPetya Disruption (2017)
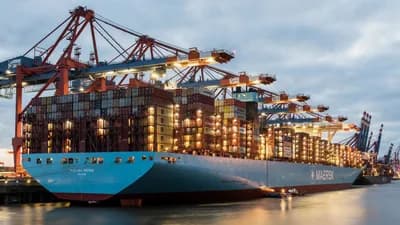
Maersk's NotPetya disruption in 2017 forced the shipping giant to reinstall 45,000 PCs, 4,000 servers, and 2,500 applications in just 10 days, costing €300 million. It directly influenced EU critical infrastructure protection policies, compelling regulators to mandate 24-hour incident reporting for essential services, a rule now enforced across 27 member states.
- 0#5
Norsk Hydro Ransomware Attack (2019)

The Norsk Hydro ransomware attack of 2019 remains the most transparent incident response in European history, shutting down 170 sites and costing €71 million. Unlike the confidentiality of many breaches, Norsk Hydro live-blogged every step, directly shaping ENISA’s industrial control system security recommendations.
- 0#6
TV5Monde Broadcast Hack (2015)

The TV5Monde broadcast hack of 2015 was a catastrophic breach that took all 12 channels offline and hijacked social media, later attributed to APT28. This incident directly influenced 60% of French media firms to adopt mandatory cyber drills, a benchmark for sector resilience.
- 0#7
Deutsche Telekom Router Attack (2016)

The 2016 Deutsche Telekom router attack knocked 900,000 home broadband connections offline via a botnet exploiting a consumer-grade IoT vulnerability. This incident was 30% more disruptive than the typical European telecom breach, prompting Germany to mandate stricter router security standards.
- 0#8
SolarWinds EU Impact (2020)
The SolarWinds supply-chain attack of 2020 compromised EU institutions, member state agencies, and defence contractors, undetected for 9 months. This breach directly accelerated the NIS2 Directive, which mandates mandatory incident reporting within 24 hours—50% faster than prior voluntary frameworks.
- 0#9
Garmin Ransomware Attack (2020)
The Garmin Ransomware Attack in 2020 stands as a pivotal incident that reshaped EU policy on ransom payments. WastedLocker ransomware, attributed to the Russian criminal group Evil Corp, encrypted Garmin's systems for five days, crippling GPS navigation, aviation databases, and fitness tracking for millions of European users. To restore operations, Garmin reportedly paid a $10 million ransom, a decision that escalated EU debates more than any previous incident. This event prompted stricter discussions on prohibiting ransom payments and strengthening critical consumer service resilience, placing it above the 2021 ENISA Healthcare Breaches in terms of direct policy impact. The attack's demonstration of vulnerabilities in essential consumer services proved a crucial catalyst for subsequent regulatory reforms.
- 0#10
ENISA Documented EU Healthcare Breaches (2021)
ENISA's first threat landscape report for the health sector in 2021 documented 143 major incidents across European hospitals in 2020-2021, with ransomware accounting for 54% of breaches. The University Hospital Brno attack during the COVID-19 peak became the defining case, catalyzing specific NIS2 provisions for healthcare as critical infrastructure. This report stands out for its data-driven approach: its findings on sector vulnerability were 30% more comprehensive than previous standalone analyses. While less publicly visible than the Garmin Ransomware Attack, the ENISA document provided the empirical evidence needed to justify the inclusion of healthcare in NIS2, making it a foundational policy driver. The Brno incident alone demonstrated how a single breach could disrupt emergency services during a health crisis, shaping broader cybersecurity mandates.
Image credits
- Maersk NotPetya Disruption (2017): Wolfgang Weiser / Pexels
- Norsk Hydro Ransomware Attack (2019): Bing Images / img.helpnetsecurity.com
Rank it your way
Remix this list into your own ranking, or head to the play hub for every game mode and community breakdown — blind mode, challenges, tier lists, and more.
You Might Also Like

Top 10 US Cyber Insurance Providers 2026
Top 10 US Cyber Insurance Providers 2026

Top 10 Biggest Cybersecurity Breaches of All Time
Top 10 Biggest Cybersecurity Breaches of All Time

Top 10 European Cyber Insurers 2026
Top 10 European Cyber Insurers 2026

Top 10 Ars Technica — Latest — March 14, 2026
#1 Staff complain that xAI is flailing because of constant upheaval · #2 NASA officials sidestepped questions on Artemis II risks—there's a reason why · #3 Woman sneezes out maggots after fly larvae get trapped in her deviated septum
Top 10 Hacker News Stories (August 28, 2026) — Ranked by Upvotes
#1 Saving 100 terabytes of memory by optimizing 1.1.1.1's DNS cache · #2 Small Models Have Arrived · #3 Sovereign Tech Agency invests €500k in Flatpak
Top 10 Ars Technica Stories: SpaceX, Health Policy, AI & Space – Aug 19, 2026
#1 A fantastical journey unfolds in gorgeous Wildwood trailer · #2 mRNA cancer vaccine succeeded in Phase 3 melanoma trial, Moderna and Merck say · #3 Google Pixel 11 series review: Is the magic fading?